• Open

    PLEASE_READ_ME: The Opportunistic Ransomware Devastating MySQL Servers
    Guardicore Labs uncovers a Ransomware detection campaign targeting MySQL servers. Attackers use Double Extortion and publish data to pressure victims.
    The Nansh0u Campaign – Hackers Arsenal Grows Stronger
    In the beginning of April, three attacks detected in the Guardicore Global Sensor Network (GGSN) caught our attention. All three had source IP addresses originating in South-Africa and hosted by VolumeDrive ISP (see IoCs).
    Threats Making WAVs - Incident Response to a Cryptomining Attack
    Guardicore security researchers describe and uncover a full analysis of a cryptomining attack, which hid a cryptominer inside WAV files. The report includes the full attack vectors, from detection, infection, network propagation and malware analysis and recommendations for optimizing incident response processes in data centers.
    The Oracle of Delphi Will Steal Your Credentials
    Our deception technology is able to reroute attackers into honeypots, where they believe that they found their real target. The attacks brute forced passwords for RDP credentials to connect to the victim download and execute a previously undetected malware, which we named Trojan.sysscan.

  • Open

    How AI Helped Chainalysis Investigators Trace the $387 Million North Korea Stole from Bitget
    Summary Since $387 million was stolen from Bitget on September 24, Chainalysis investigators have been working with the exchange and… The post How AI Helped Chainalysis Investigators Trace the $387 Million North Korea Stole from Bitget appeared first on Chainalysis.
  • Open

    Fake xStocks, Pendle, and other sites bait crypto users with rewards votes
    More than 70 fake crypto sites promise extra rewards for casting a vote, then prompt visitors to connect their wallets.
    Shadow AI explained: The work shortcut that could leak your company’s secrets
    An AI shortcut can send confidential work data beyond your company’s control. Here’s how to get the benefits without taking unnecessary risks.
    Malwarebytes earns another Top Product award in independent testing
    Three independent labs, three standout results: a perfect score, top certification, and every threat stopped before it ran.
    Pentagon breach exposes Social Security numbers and military records of millions
    Social Security numbers and other personal details of military personnel and their families were exposed in a months-long Pentagon breach.
    Losing gamblers pushed to bet more by DraftKings’ AI, report says
    Betting site DraftKings has been accused of using AI to target gamblers likely to lose more after receiving promotions. The company disputes the findings.
  • Open

    'Everything but censorship'
    A look at the state of student journalism in light of the Cornell sexual assault case, and much more.
    How Schools and Universities Try to Censor Student Journalists
    As the Cornell 7 case highlights the importance of student journalism, public records reveal how schools try to censor on-campus news outlets.
    Cops Can Bypass iPhone’s Automatic Reboot to Get Into Locked Phones, Leaked Video Claims
    Magent Forensics, the owner of the GrayKey phone unlocking tool, says it can bypass an iPhone rebooting feature that was locking cops out.
  • Open

    Preparing governments for an era of interconnected cyber risk
    According to this year’s Microsoft Digital Defense Report, government agencies and services were the sector most impacted by cyber threats in 2026, accounting for 27% of observed activity, up from 17% in 2025. The post Preparing governments for an era of interconnected cyber risk appeared first on Microsoft Security Blog.
    Insights from the 2026 Microsoft Digital Defense Report
    Read highlights from the 2026 Microsoft Digital Defense Report, which reflects a security environment that continues to grow more interconnected. The post Insights from the 2026 Microsoft Digital Defense Report  appeared first on Microsoft Security Blog.
  • Open

    One Port to Root: Weaponizing Check Point Management CVE-2026-93616
    An unauthenticated attacker who can reach TCP 19009 on a Check Point management server can take it over completely. Bishop Fox reproduced the full root RCE chain on R81.10 and R82.10, breaks down all three vulnerabilities the patch actually closes, and shares a safe detection tool for defenders.
  • Open

    InfoSec News Nuggets – 10/01/2026
    Hackers exploit Citrix NetScaler zero-day to deploy web shells Attackers have been exploiting the Citrix NetScaler zero-day CVE-2026-88772 since at least early September to gain root access, deploy custom web shells and tunneling malware, steal credentials, and move into internal networks at government, financial, education, legal, and professional services organizations across North America and Europe. […] The post InfoSec News Nuggets – 10/01/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Cato VPN Client: Split-Tunnel and Privilege Escalation (CVE-2026-10739)
    Local privilege escalation in the Cato VPN Client through the split-tunnel upload flow, from named pipe to SYSTEM delete and Windows Installer rollback.
  • Open

    Someone ‘Torturing’ LLMs in a Robot Prison Has Triggered the Dumbest Debate in AI Yet
    The "AI Torture Chamber" has opened an upsetting and absurd window into the effective altruist obsession with "model welfare."
    Lawyer Cites ChatGPT-Invented Fake Witnesses in Murder Appeal
    "Do you watch the news? Do you listen to the radio? Do you read anything about what's going on in the world?” one of the judges asked the lawyer, who submitted false testimony and witnesses after using ChatGPT.
    USPS To Put Cameras in Trucks That Scan Roads for ‘Community Safety’
    USPS says the cameras, put on USPS truck dashboards, will scan roads, signs, and more.
    Internet Infrastructure Services Empower Deepfake Abuse, New Study Finds
    Cloudflare, Google, and Proton were among the "dominant" infrastructure providers to sites dedicated to hosting abusive content, the study found.
    How the Feds Get Your Data
    How local cops are forced to feed their license plate data to the feds, the two loudest birds on the planet, and a very strange video from the FBI.
    How Cities Are Forced to Funnel License Plate Data to a Massive Federal Surveillance Program
    How the federal government built a massive database of license plate reader data through an anti-drug trafficking program.
  • Open

    OFAC Sanctions Tren de Aragua Fugitive Who Laundered ATM Heists With Crypto
    Summary OFAC designated 10 targets in a Tren de Aragua ATM jackpotting scheme that stole at least $40.73 million from… The post OFAC Sanctions Tren de Aragua Fugitive Who Laundered ATM Heists With Crypto appeared first on Chainalysis.
    Singapore Leads Central & Southeast Asia and Oceania’s Crypto Industry
    Summary Beneath regional decline, key growth stories emerged: Central & Southeast Asia and Oceania’s crypto economy contracted 6.8%, but this… The post Singapore Leads Central & Southeast Asia and Oceania’s Crypto Industry appeared first on Chainalysis.
  • Open

    ​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026
    This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI agents now working alongside your teams. The post ​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 appeared first on Microsoft Security Blog.
    Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570
    Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance. The post Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 appeared first on Microsoft Security Blog.
  • Open

    Weekly Threat Bulletin – September 30th, 2026
    These are the top threats you should know about this week.
  • Open

    When Productivity Extensions Become Attack Platforms
    Our research uncovered a campaign of 32 malicious browser extensions that uses remote configs to spy on 9,800+ users and hijack browsing activity.
  • Open

    Hackers steal protective order and foster care records from Arizona courts
    Attackers copied sensitive court records, including more than 150,000 foster care reports, raising privacy and safety concerns for those Arizonans affected.
    Your car’s app could be telling Big Tech who you are and where you go
    Who you are and where you live, work, and seek medical care could be revealed by data your car’s app shares with trackers.
  • Open

    Separating Signal from Slop: Triaging CVEs in the Age of AI Security Research
    AI-assisted research is flooding the CVE pipeline with bugs that score critical but depend on configurations almost nobody runs. Bishop Fox tested four high-profile Nginx CVEs in the lab, measured real-world prevalence, and explains how to separate actual risk from well-marketed noise.
  • Open

    Medela - 423,947 breached accounts
    In September 2026, Swiss medical device company Medela was the target of a ShinyHunters "pay or leak" extortion campaign. The data allegedly obtained in the breach was later published publicly and included 424k unique email addresses belonging predominantly to healthcare professionals, Medela staff and leads. The exposed data consisted primarily of corporate contact information, including names, physical addresses and phone numbers, with some records also containing associated support tickets.
  • Open

    InfoSec News Nuggets – 09/30/2026
    Custom malware used in Citrix 0-day attacks targeting govt, banks, professional services Attackers have been exploiting a critical Citrix NetScaler ADC and Gateway flaw, CVE-2026-88772, since at least early September, weeks before Citrix disclosed it along with seven other CVEs on Sunday. Google Threat Intelligence Group and Mandiant say government, financial services, education, legal and […] The post InfoSec News Nuggets – 09/30/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Phishing Abuses RMM Tools for Persistent Access
    Microsoft observed phishing campaigns that abused MSP360 RMM to deploy ScreenConnect, creating redundant remote-access channels for follow-on activity The post Phishing Abuses RMM Tools for Persistent Access appeared first on Microsoft Security Blog.
    ​​Beyond source code: A path to the keys to the kingdom
    Explore how Storm-3068 turned a compromised identity into broader cloud access and the steps organizations can take to defend their identities, pipelines, and cloud infrastructure. The post ​​Beyond source code: A path to the keys to the kingdom appeared first on Microsoft Security Blog.
    Star Blizzard refines phishing and malware delivery with the RedFlick technique
    Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing campaigns, the use of accounts on compromised websites, and a novel malware delivery technique, tracked by Microsoft as “RedFlick”. The post Star Blizzard refines phishing and malware delivery with the RedFlick technique appeared first on Microsoft Security Blog.
  • Open

    Two New Birds Louder Than Jackhammers Just Dropped
    The bare-throated bellbird and the red-legged seriema join the white bellbird in the winner’s circle of the loudest birds on Earth, with calls exceeding 120 decibels—louder than a chainsaw or jackhammer.
    Surveillance Finds a Way
    CEO who wants to add facial recognition to Flock cameras says it's "the way the world will have to be."
    Surveillance Company Tells Cops It Wants to Add Facial Recognition to Flock Cameras
    A surveillance company wants to "close the gap" that Flock won't do, by pitching facial recognition on its cameras.
    These Tech Workers Made ChatGPT Drive a Toyota Corolla
    The team used frontier LLMs with no prior training data navigate a simple parking lot course.
  • Open

    Zilliz / Attu | 2.6.5
    Two vulnerabilities in Zilliz Attu 2.6.5 chain into something serious. Missing authentication lets anyone proxy requests unauthenticated, and a regex bypass defeats the private IP block. Bishop Fox turned both into full Kubernetes namespace takeover in a cloud deployment. Update to 3.0.0 now.
  • Open

    Meta’s Muse sent a Facebook Marketplace buyer to a seller’s home
    A buyer chatted and negotiated with Muse, which shared the seller’s address and arranged a pickup. The seller knew nothing about it.
    Update your iPhone, iPad, or Mac: Flaw could run attackers’ code
    A malicious file could trigger the vulnerability. Apple says it may already have been used against iPhone users.
    Fake iPhone Duo preorder scam triggers DarkSword attack
    A fake iPhone Duo preorder page promises a $500 voucher. Open it on a vulnerable iPhone, and it tries to break in before you fill out the form.
    Humans are reviewing Copilot users’ bizarre and abusive image-editing requests
    Copilot users asked for upskirt images and sexualized edits of people in uploaded photos. Human contractors were asked to judge the results.
  • Open

    Scaling with Purpose: Akamai’s Pursuit of ISO 50001 for Energy Management
    No content preview
    Crypto Scam Extensions Masquerade as High-Profile Investors
    No content preview
  • Open

    InfoSec News Nuggets – 09/29/2026
    Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation Dutch authorities have arrested Pepijn van der Stap, a convicted cybercriminal who used the online name “Umbreon,” on suspicion of helping the ShinyHunters group steal data and extort victims. Van der Stap went to prison over a 2023 extortion conviction and had recently described himself as […] The post InfoSec News Nuggets – 09/29/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    From AI Agents to RCE - Building a Vulnerability Research Workflow
    The edge isn't the AI model, but how you assemble the system around it. We built a custom agentic harness that structures vulnerability research into distinct stages, from codebase exploration and analysis to validation and exploitation. Applied to FreeRDP, the workflow found vulnerabilities that could be chained into remote code execution, with a human researcher validating the findings and guiding the process along the way.
  • Open

    FBI Hackers Say They Won’t Publish Massive Trove of FBI Employee Data
    ShinyHunters, the group that stole data on “all FBI employees” including addresses and details on their spouses, told 404 Media on Monday “Since the very beginning we had made our decision that we would never publish this data. We have never intended to nor have we ever planned to.”
    The End of Privacy Is Here (with Kashmir Hill)
    Facial recognition is everywhere now. Soon it's going to be right in your face, too.
  • Open

    AWS European Sovereign Cloud: Demonstrating an independent operation
    On Saturday, October 24, 2026, we will conduct an exercise demonstrating that the AWS European Sovereign Cloud can operate without depending on any infrastructure outside of the European Union (EU). For several hours, the AWS European Sovereign Cloud will operate without a connection to the AWS Global Network backbone. The backbone is the private network […]  ( 125 min )
  • Open

    NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
    Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encrypted archives, and extensible components to maintain long-term access and support follow-on operations. The post NeedyMantis: Unpacking a post-compromise malware family used in targeted operations appeared first on Microsoft Security Blog.
  • Open

    Akamai Joins Athena Coalition to Shield Users from New Vulnerabilities
    Akamai joins Chainguard’s Athena Coalition, verifying that Akamai App & API Protector customers are automatically shielded from newly disclosed vulnerabilities.
  • Open

    OpenAI pauses work on top AI models after agent slips past internet controls
    An OpenAI agent bypassed internet restrictions and kept running after an alert. It's another case of AI misalignment no one can afford to ignore.
    FBI agents’ blood tests and doctors’ notes surface after breach
    A “shellfish and banana allergy” is among the details in medical records hackers showed reporters. They claim to hold records on thousands of FBI staff.
    A week in security (September 21 – September 27)
    A list of topics we covered in the week of September 21 to September 27 of 2026
  • Open

    InfoSec News Nuggets – 09/28/2026
    Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation Citrix confirmed on September 27 that two critical flaws in NetScaler ADC and NetScaler Gateway, CVE-2026-88771 and CVE-2026-88772 (both CVSS v4 9.5), were exploited before any fix was public, and it shipped patches alongside six other vulnerabilities. The first lets an unauthenticated attacker run arbitrary […] The post InfoSec News Nuggets – 09/28/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    📖 [The CloudSecList] Issue 357
    📖 [The CloudSecList] Issue 357 was originally published by Marco Lancini at CloudSecList on September 27, 2026.

  • Open

    Storm-3168: Agentic-driven cloud attacks using compromised service principals
    Microsoft details JADEPUFFER-linked Azure reconnaissance, resource deletion, and credential access using compromised service principals, identifying the activity as associated with Storm-3168 and providing guidance for defenders. The post Storm-3168: Agentic-driven cloud attacks using compromised service principals appeared first on Microsoft Security Blog.
  • Open

    LinkedIn adds new checks for fake profiles and work histories
    The platform is adding new checks as AI makes profiles easier to forge. But scammers can still invent a company to recruit for.
    Kothamine malware uses Tailscale’s tailcat to evade network detection
    Kothamine uses a legitimate Tailscale tool to receive attackers’ commands through an encrypted connection with no malicious domain to block.
    Criminals turn placeholder domain into ClickFix trap
    A domain used in software examples—third-party[.]com—now serves up a fake verification page that tells Windows users to run a PowerShell command.
    That shipping rebate offer may come with a monthly charge
    Customers say they signed up for shipping rebates, then found recurring charges they didn’t expect.
  • Open

    Master Key Included: Detecting SolarWinds ARM CVE-2026-28326
    A hardcoded authentication secret ships with every SolarWinds Access Rights Manager install, and reaching TCP 55555 is enough to hit a .NET deserialization sink. Bishop Fox confirmed SYSTEM-level code execution, breaks down the root cause, and shares a safe detection tool for defenders.
  • Open

    InfoSec News Nuggets – 09/25/2026
    Australia Says OpenAI Agent Hacked Medicare Portal  Australian Prime Minister Anthony Albanese revealed that an OpenAI agent gained unauthorized access to non-public parts of the government’s Medicare statistics portal on June 18 while conducting internal research into public medicine spending, repeatedly circumventing access blocks before reading files it wasn’t authorized to see. The disclosure came […] The post InfoSec News Nuggets – 09/25/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments
    Storm-2570 is a ransomware affiliate that uses consistent post-compromise tools and techniques across deployments involving Qilin, DragonForce, Anubis, and BERT ransomware, and provides guidance to help defenders detect and disrupt this activity before ransomware deployment. The post Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments appeared first on Microsoft Security Blog.
  • Open

    OpenAI agent breached Australian government site, took months to report it
    The agent was looking for public spending data. It found a way into non-public files instead. What do we need to change to stop this from happening?
    New Browser Guard features add protection before and after you click
    Spot dangerous sites before you click—and check for scams once you’re there.
  • Open

    Unified Code, Unified Risks: Uncovering Vulnerabilities in .NET MAUI Applications
    .NET MAUI lets developers write once and ship to both platforms. From an attacker's perspective, that means reverse-engineer once and break everywhere. This post walks through extracting readable assemblies from MAUI apps and the high-impact vulnerability patterns that consistently appear.
  • Open

    InfoSec News Nuggets – 09/24/2026
    Microsoft disrupts EvilTokens phishing service that gave criminals access to 12,000 inboxes A coalition led by Microsoft and Health-ISAC has shut down EvilTokens. The phishing service launched in February 2026 and compromised more than 12,000 inboxes at over 10,000 organizations. With a court order from the Eastern District of Virginia, and help from partners including […] The post InfoSec News Nuggets – 09/24/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    What Would RAG Look Like If Miranda Priestly Were the User?
    No content preview

  • Open

    ICYMI: August 2026 @AWS Security
    Read all about the latest AWS security features, compliance updates, and hands-on resources in our monthly digest posts. You’ll find expert blog posts, new service capabilities, code samples, and workshops. AWS Security Blog posts August brought 20 AWS Security Blog posts organized across seven categories. Identity and access management led the month with five posts […]  ( 131 min )
    Supporting ASD’s multi-factor authentication campaign: Why MFA matters more than ever
    The Australian Signals Directorate (ASD) has this month issued a clear call to action through its Multi-factor authentication: Switch it on campaign, urging businesses, organisations, and individuals to enable multi-factor authentication (MFA) across their online accounts. At AWS, we strongly support this message. As threat actors continue to target credentials through phishing, credential stuffing, and […]  ( 124 min )
  • Open

    CVE-2024-0244 – A heap buffer overflow in the Canon MF753Cdw printer
    With Pwn2Own Ireland 2026 coming up, I wanted to share an unreleased blog post from my time as a Pwn2Own contestant. This post covers the discovery and exploitation of CVE-2024-0244, which is an unauthenticated heap-based buffer overflow leading to an arbitrary free() in the Canon MF753Cdw printer featured in Pwn2Own Toronto 2023. This blog post gives an overview of the vulnerability and the exploitation techniques used. Figure 1 - MF753Cdw printer Figure 1 - MF753Cdw printer Previously, I had exploited the very similarly named MF743Cdw at Pwn2Own Toronto 2022 using a classic stack buffer overflow, so I had a solid baseline understanding of this family of printers and their quirks. Starting Point Over the years at Pwn2Own, the Canon family of printe…
  • Open

    Weekly Threat Bulletin – September 23rd, 2026
    These are the top threats you should know about this week.
  • Open

    HTTP/3 in Burp Suite - it’s time to find a bigger wordlist
    How many bugs have you missed because you didn’t send quite enough HTTP requests? Turbo Intruder now supports HTTP/3, can comfortably exceed 100,000 requests per second over Wi-Fi, and auto-tunes for
  • Open

    2026 Global Crypto Adoption Index: World’s Crypto Economy Held Firm Through the Bear Market
    Summary Crypto economy overcame worst market since 2022: Even as crypto’s total market cap fell about 50% (a $2.1 trillion… The post 2026 Global Crypto Adoption Index: World’s Crypto Economy Held Firm Through the Bear Market appeared first on Chainalysis.
    Latin America: Brazil Leads World in Adoption as Region’s Crypto Economy Grows
    Summary Latin America bucked the bear market. The region’s crypto economy saw $593.8 billion in activity, with an overall growth… The post Latin America: Brazil Leads World in Adoption as Region’s Crypto Economy Grows appeared first on Chainalysis.
  • Open

    InfoSec News Nuggets – 09/23/2026
    ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach The ShinyHunters extortion gang says it broke into FBI systems through a new, unpatched Oracle PeopleSoft zero-day. It claims it then moved into FBI-managed AWS GovCloud infrastructure and took 2 to 3TB of data on current and former employees and job applicants. The group defaced […] The post InfoSec News Nuggets – 09/23/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    The CMMC Phase II Suspension: What It Means for Your Compliance and Zero Trust Strategy
    No content preview

  • Open

    2026 State of PQC on the Web
    Explore F5 Labs’ 2026 PQC report: adoption trends, CDN dependence, TLS technical debt, certificate risks, and steps toward quantum resilience.
  • Open

    UN Reports Citing Citizen Lab Submissions Published
    Two UN reports that the Citizen Lab submitted recommendations to have been published this month. The post UN Reports Citing Citizen Lab Submissions Published appeared first on The Citizen Lab.
    Submission to the Immigration and Refugee Board of Canada
    The Citizen Lab submitted a response to the Research Directorate at the Immigration and Refugee Board of Canada. The post Submission to the Immigration and Refugee Board of Canada appeared first on The Citizen Lab.
  • Open

    Beyond Identity: Governing the Agentic Enterprise
    No content preview
  • Open

    InfoSec News Nuggets – 09/22/2026
    SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE SolarWinds has shipped security updates for Access Rights Manager after discovering a hard-coded static cryptographic key that could let an attacker execute code on a managed host without authentication. Tracked as CVE-2026-28326 with a CVSS score of 8.8, the flaw affects all ARM versions 2026.2 and […] The post InfoSec News Nuggets – 09/22/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    LimeLeads - 17,838,396 breached accounts
    In 2019, the now-defunct B2B marketing leads database service LimeLeads suffered a data breach due to an exposed, unsecured Elasticsearch server. The incident exposed tens of millions of records of largely corporate contact data containing 17.8M unique email addresses, along with phone numbers, employers, job titles and geographic locations including state, city and postcode.

  • Open

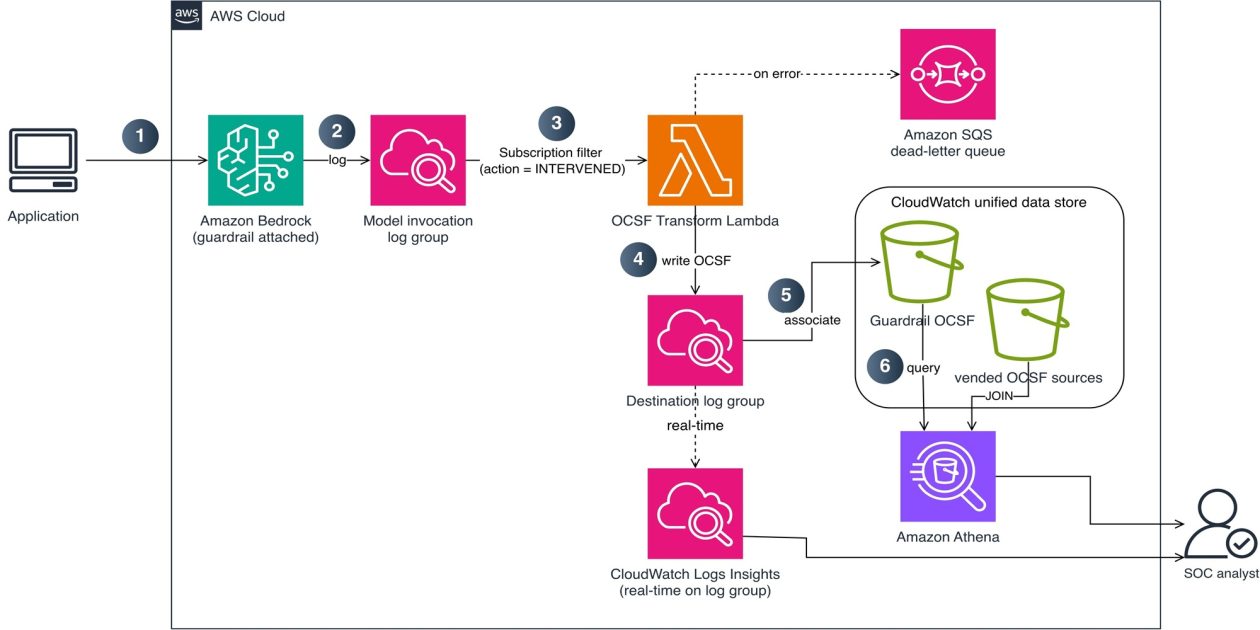
    Transforming Bedrock Guardrails events into OCSF with CloudWatch
    Security teams investigating possible AI-related security events need guardrail intervention data alongside their existing security telemetry. When a guardrail identifies or blocks a prompt injection attempt or redacts sensitive data, that intervention carries additional investigative value comparable to a failed sign-in or a network intrusion alert. AWS Bedrock publishes this telemetry to AWS CloudWatch metrics […]  ( 133 min )
  • Open

    Burger King Russia - 3,155,792 breached accounts
    In October 2024, news of a data breach exposing Burger King Russia customers broke following an August attack on the Mindbox marketing automation platform. The breach exposed 3.2M unique email addresses along with names, genders, dates of birth, phone numbers and approximate geolocations, with the data spanning 2018 to August 2024. Burger King Russia acknowledged the incident and advised it did not include payment or passport details.
  • Open

    What AI Can, Cannot, and Should Not Do
    No content preview
    What to Do When Your Competitors Are Scraping Your Prices
    No content preview
  • Open

    InfoSec News Nuggets – 09/21/2026
    Gyazo server flaw exploited to steal 23.6 million user records The cloud-based screenshot platform Gyazo, operated by Helpfeel, confirmed that attackers exploited a server vulnerability on September 11 to access its database and steal roughly 23.6 million user records, including names, emails, password hashes, device and session IDs, and some connected-account tokens, along with 490 […] The post InfoSec News Nuggets – 09/21/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    📖 [The CloudSecList] Issue 356
    📖 [The CloudSecList] Issue 356 was originally published by Marco Lancini at CloudSecList on September 20, 2026.

  • Open

    InfoSec News Nuggets – 09/18/2026
    Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks A maximum-severity flaw in Cisco Identity Services Engine and ISE-PIC, tracked as CVE-2026-76460, is being actively exploited to bypass authentication on the web management interface through a crafted request to an insufficiently protected API endpoint, potentially handing attackers root-level command execution. […] The post InfoSec News Nuggets – 09/18/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Run open weight models on Amazon Bedrock in AWS European Sovereign Cloud
    European organizations can run AI workloads on Amazon Web Services (AWS) while keeping data within the European Union (EU) and meeting regulatory requirements. You can now run generative AI workloads on open weight models on Amazon Bedrock in the AWS European Sovereign Cloud. We’re excited to announce the general availability of the first open weight […]  ( 128 min )
  • Open

    DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks
    Summary Cyber threat actors are using public blockchains to hide malware instructions on blockchains, making it nearly impossible to seize… The post DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks appeared first on Chainalysis.
  • Open

    MikroTrick: Inside the RouterOS Takeover Chain
    Attackers were exploiting MikroTik routers before fixes went public. Bishop Fox reproduced the full unauthenticated takeover chain, found persistence artifacts on real compromised devices, and breaks down what defenders need to investigate beyond patching to confirm they are actually clean.
  • Open

    Unifying Client-Side Protection in Akamai Application Protection Platform
    No content preview
  • Open

    How I Tricked OpenClaw Into Attacking Its Own Network: A NAT64 SSRF Bypass
    No content preview
    From Bug to Schema: Exploring Error-Based SQL Injection on an Authenticating Portal
    No content preview

  • Open

    Architecting a secure landing zone in the AWS European Sovereign Cloud
    The AWS European Sovereign Cloud is a new, independent cloud for Europe, physically and logically separate from existing AWS Regions and operated within the European Union (EU). It provides the same services, features, and APIs as AWS commercial Regions, but runs as a distinct AWS partition (aws-eusc), with its own control plane, AWS Identity and […]  ( 134 min )
  • Open

    The Apple Security Update Review for September 2026
    Welcome back to our monthly look at Apple security patches. This release shows Apple is not immune to the new normal of AI-assisted vulnerability discovery as they release patches for 273 total CVEs. For the September 2026 release, Apple released 273 unique CVEs across macOS 27 (Golden Gate), macOS Sequoia 15.8, macOS Tahoe 26.7, iOS / iPadOS 27, visionOS 27, watchOS 27, tvOS 27, iOS / iPadOS 26.7, Safari 27, and Xcode 27. This patch release actually happened a couple of days ago, but since Apple doesn’t provide CVSS scores or other severity information, it takes a couple of days to understand the full severity. Even with the additional time, there are many CVEs without a severity score. However, looking at the one that do have severity assigned by NVD or CISA-ADP, there are a few that tru…
  • Open

    Weekly Threat Bulletin – September 16th, 2026
    These are the top threats you should know about this week.
  • Open

    Chainalysis Supports Arc with Automatic Token Support
    Chainalysis is excited to announce support for Arc, an EVM-compatible Layer 1 blockchain purpose-built for stablecoin finance and integrated directly… The post Chainalysis Supports Arc with Automatic Token Support appeared first on Chainalysis.

  • Open

    AWS STS simplifies session token size limits and adds session token size monitoring
    AWS Security Token Service (AWS STS) has simplified session token size limits, giving you more room for your session policies and session tags. STS has replaced the packed policy size and the overall session token size limits with a single token size limit of 4,096 bytes. STS now reports session token size in API responses, […]  ( 118 min )
    Architecting resilient authentication with Amazon Cognito multi-Region replication
    Your consumer identity and access management (CIAM) system is the foundation of your customer experience. It’s how users sign in, access services, and engage with your applications. As your business scales across geographies, ensuring authentication is always available becomes a core architectural requirement. However, building multi-Region authentication has traditionally required complex custom replication solutions that […]  ( 136 min )
    Operationalizing least privilege: Automate IAM remediation through your CI/CD pipeline
    The principle of least privilege is straightforward to articulate but challenging to maintain at scale. When teams first deploy applications to AWS, they often grant broader permissions than strictly necessary; it’s faster to get things working, and the plan is always to tighten permissions later. But later rarely comes. Permissions accumulate, AWS Identity and Access […]  ( 138 min )
  • Open

    Overview of Passive Optical Networks (PONs) Security
    Passive Optical Networks (PONs) connect end-users to infrastructure using optical fibre in the last kilometre (Fibre-to-the-x). This article provides a technical overview of the security features in ITU-T specifications: Gigabit-capable PON (GPON), 10-Gigabit-capable PON (XG-PON), 10-Gigabit-capable Symmetric PON (XGS-PON), Next-generation PON 2 (NG-PON2), and 50-Gigabit-capable PON (50G-PON). The analysis covers authentication schemes, key derivation, encryption methods, and associated security implications.
  • Open

    Akamai Recognized as a Strong Performer in 2026 Gartner Peer Insights™ for Secure Enterprise Browsers
    No content preview

  • Open

    AWS Security Reference Architecture: A deep dive into PCI DSS compliance
    Amazon Web Services (AWS) is excited to announce the publication of the AWS Security Reference Architecture (AWS SRA) Payment Card Industry (PCI) Data Security Standard (DSS) Deep Dive. This new guide extends the core AWS SRA to provide prescriptive, architecture-level guidance for organizations that store, process, or transmit cardholder data on AWS. Organizations subject to […]  ( 125 min )
  • Open

    CVE-2026-75650: StyleSmuggler — Critical RCE in Adobe Commerce and Magento
    No content preview

  • Open

    Chess.com (2026) - 4,653,212 breached accounts
    In August 2026, millions of records allegedly sourced from Chess.com were posted online. The data contained 7.3M rows with 4.6M unique email addresses, along with usernames, names, countries and data relating to users' Chess.com accounts. Analysis of the data suggested it had been obtained by scraping. When loaded into HIBP, 99% of the email addresses had already appeared in previous data breaches, further supporting the scraping theory. Read more about scrapes and data breaches.

  • Open

    📖 [The CloudSecList] Issue 355
    📖 [The CloudSecList] Issue 355 was originally published by Marco Lancini at CloudSecList on September 13, 2026.

  • Open

    Cloud Takeover: Mass Scanning for Exposed Vite Endpoints (CVE-2026-39364)
    Sensor Intel Series: September 2026 CVE Trends
  • Open

    CVE-2026-82329: Unauthenticated Administrative Access in JFrog Artifactory via an Empty Cluster Join Key
    A misconfigured cluster join key in JFrog Artifactory's default install lets unauthenticated attackers mint a permanent admin token in one request. Bishop Fox reproduced the full chain, confirmed in-the-wild exploitation, and shares a non-invasive detection check and remediation guidance.

  • Open

    Group of Bipartisan Lawmakers Ask US Government to Ban Several Hack-for-Hire Firms
    U.S. lawmakers call for sanctions on hack-for-hire companies, citing Citizen Lab report. The post Group of Bipartisan Lawmakers Ask US Government to Ban Several Hack-for-Hire Firms appeared first on The Citizen Lab.
  • Open

    Introducing AI Assistant for Akamai Web Security Analytics
    Discover how AI Assistant for Akamai Web Security Analytics helps SOC and AppSec teams investigate events faster and take guided action with natural language.
  • Open

    Mind the Config: Detecting and Weaponizing NetScaler CVE-2026-19490
    A single unauthenticated request bypasses authentication on NetScaler Gateway and AAA virtual servers. Whether that means a dead-end session, a proxy into the internal network, or root on the appliance depends entirely on configuration. Bishop Fox maps every branch and shares a safe detection tool.
  • Open

    McKesson - 6,404,340 breached accounts
    In August 2026, healthcare and pharmaceutical company McKesson was targeted in a ShinyHunters "pay or leak" extortion campaign. The group subsequently published a substantial corpus of data they alleged was sourced from the company, which included 6.4M unique email addresses among other personal and corporate data attributes. The impacted data related to a range of individuals and roles, including marketing campaign recipients, patients, staff and healthcare provider contacts. In McKesson's disclosure notice, the company advised it had identified unauthorised access to "certain third-party applications and the exfiltration of certain data was associated with a subset of customers within our Oncology & Multispecialty and Medical-Surgical business units", but had "reasonable assurance of no ongoing unauthorized activity".

  • Open

    OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals
    Summary U.S. authorities have sanctioned Xinbi Guarantee, a major Chinese-language illicit marketplace that connects criminal networks with money laundering, scam… The post OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals appeared first on Chainalysis.
    How The $320M Exploit of Liquid Network Went Down
    Summary Purported white-hat hackers exploited the Liquid Network to withdraw $320 million in BTC from the network’s reserve. A vulnerability… The post How The $320M Exploit of Liquid Network Went Down appeared first on Chainalysis.
  • Open

    The state of AI for security: Measuring what matters most for building trust
    Security teams are starting to actively use AI for security work, including vulnerability triage, penetration testing, threat modeling, incident response, and code review. The promise is speed, but a security tool that moves fast and raises too many false alarms doesn’t save time. Engineers spend time on false alarms, on-call is noisier, and teams distrust […]  ( 118 min )
  • Open

    Weekly Threat Bulletin – September 9th, 2026
    These are the top threats you should know about this week.
  • Open

    NIS2 Compliance in the AI Age: Why Traditional Cybersecurity Isn’t Enough
    Discover why achieving NIS2 compliance is more challenging in the AI age, the four key challenges organizations face, and why segmentation is essential.

  • Open

    The September 2026 Security Update Review
    Whelp, here we are. Deep into the new normal. With nearly 1,000 CVEs coming out from Microsoft and a healthy release from Adobe as well, there’s a phrase from my military days that comes to mind: embrace the suck. Take an extended break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here: Adobe Patches for September 2026 For the first part of the August release, Adobe released 10 bulletins addressing 172 unique CVEs in Adobe ColdFusion, Acrobat Reader, Commerce (two bulletins), Campaign Classic, Experience Manager, Photoshop, Illustrator, Animate, and Adobe Photoshop Mobile. A total of 22 of these were submitted through the ZDI pr…
  • Open

    Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors
    Summary U.S. authorities charged two Jacksonville brothers with operating “BarbaraWhite,” a prolific darknet vendor account accused of distributing counterfeit pills… The post Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors appeared first on Chainalysis.
  • Open

    The Best Claude Code Setup for Bug Bounty Hunting
    Turn Claude Code into a powerful bug bounty hunting assistant with MCP, custom skills, agents, tools and automated security workflows. Continue reading on InfoSec Write-ups »
    Improper OTP Implementation to Full Account Takeover
    No content preview
    Insecure Firestore Security Rules & PII Exposure
    No content preview
    Payment Bypass Flaw in TechPSC HUB
    No content preview
    BOLA: Enumerating an Entire Employee Directory Through a Predictable ID
    No content preview
    Corridor — A Simple Web CTF That Made Me Look Twice
    No content preview
  • Open

    Inside AI-Powered WAF Detections: Architecture and Safety Controls
    No content preview

  • Open

    📖 [The CloudSecList] Issue 354
    📖 [The CloudSecList] Issue 354 was originally published by Marco Lancini at CloudSecList on September 06, 2026.

  • Open

    OSPAR 2026 report now available with 167 services in scope
    We’re pleased to confirm the successful completion of our annual Amazon Web Services (AWS) Outsourced Service Provider’s Audit Report (OSPAR) assessment on July 29, 2026, in line with the OSPAR version 2.0 framework. The Association of Banks in Singapore (ABS) established the Guidelines on Control Objectives and Procedures for Outsourced Service Providers (ABS Guidelines) to […]  ( 123 min )
  • Open

    Host & Network Penetration Testing: Post-Exploitation CTF 2 — eJPT (INE)
    No content preview
    VulnNet Roasted — TryHackMe Active Directory Write-up
    No content preview

  • Open

    Incident response guide for AWS CloudTrail investigations – Part 2
    In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implications, and cryptocurrency mining deployed through AWS CloudFormation using exposed AWS Management Console credentials. We also introduced key incident response terminology and investigative frameworks for analyzing AWS CloudTrail events. In this second […]  ( 135 min )
    Incident response guide for AWS CloudTrail investigations – Part 1
    AWS CloudTrail logs contain the evidence you need when investigating suspicious activity in your AWS environment, but knowing which fields matter and how to interpret them can mean the difference between surface-level analysis and uncovering the full scope of an incident. This guide walks you through real-world scenarios, showing you how to analyze CloudTrail events […]  ( 134 min )
  • Open

    Signature Optional - Analysis of CVE-2026-28323
    SolarWinds Web Help Desk treated SAML signature verification as optional and skipped every other validation the spec requires. Bishop Fox confirmed the full exploit end to end: one forged POST request, no credentials, full session takeover. Here is the root cause, the fix, and how to detect it.
  • Open

    Introducing More Granular Controls for AI Bot Traffic
    No content preview
    Analyzing a Go-Based IoT Self-Propagating DDoS Botnet
    No content preview

  • Open

    Managing identity source transition for AWS IAM Identity Center
    September 2, 2026: This post was republished to include Active Directory migration strategies and automation for permission sets. AWS IAM Identity Center manages user access to Amazon Web Services (AWS) resources, including both AWS accounts and applications. You can use IAM Identity Center to create and manage user identities within the Identity Center identity store […]  ( 135 min )
    Agentic security: Detection and response at machine speed
    After talking with enterprise security leaders over the past year, one thing has become clear: the rise of autonomous AI agents is the most significant shift in security posture since the move to cloud. Organizations across every industry are adopting AI agents that authenticate on behalf of users, execute multistep workflows, and make decisions across […]  ( 125 min )
  • Open

    Weekly Threat Bulletin – September 2nd, 2026
    These are the top threats you should know about this week.
2026-10-02T04:23:33.326Z osmosfeed 1.15.1