• Open

    The Oracle of Delphi Will Steal Your Credentials
    Our deception technology is able to reroute attackers into honeypots, where they believe that they found their real target. The attacks brute forced passwords for RDP credentials to connect to the victim download and execute a previously undetected malware, which we named Trojan.sysscan.
    The Nansh0u Campaign – Hackers Arsenal Grows Stronger
    In the beginning of April, three attacks detected in the Guardicore Global Sensor Network (GGSN) caught our attention. All three had source IP addresses originating in South-Africa and hosted by VolumeDrive ISP (see IoCs).
    PLEASE_READ_ME: The Opportunistic Ransomware Devastating MySQL Servers
    Guardicore Labs uncovers a Ransomware detection campaign targeting MySQL servers. Attackers use Double Extortion and publish data to pressure victims.
    Threats Making WAVs - Incident Response to a Cryptomining Attack
    Guardicore security researchers describe and uncover a full analysis of a cryptomining attack, which hid a cryptominer inside WAV files. The report includes the full attack vectors, from detection, infection, network propagation and malware analysis and recommendations for optimizing incident response processes in data centers.

  • Open

    ICYMI: August 2026 @AWS Security
    Read all about the latest AWS security features, compliance updates, and hands-on resources in our monthly digest posts. You’ll find expert blog posts, new service capabilities, code samples, and workshops. AWS Security Blog posts August brought 20 AWS Security Blog posts organized across seven categories. Identity and access management led the month with five posts […]  ( 121 min )
    Supporting ASD’s multi-factor authentication campaign: Why MFA matters more than ever
    The Australian Signals Directorate (ASD) has this month issued a clear call to action through its Multi-factor authentication: Switch it on campaign, urging businesses, organisations, and individuals to enable multi-factor authentication (MFA) across their online accounts. At AWS, we strongly support this message. As threat actors continue to target credentials through phishing, credential stuffing, and […]  ( 114 min )
  • Open

    FBI Hack Exposed FBI’s Own Hacking Unit
    The FBI's Remote Operations Unit (ROU) is a highly secretive team of hackers making exploits and tools to break into target’s devices. Some of its members just got exposed.
    An Invisible Force Has a Mysterious Effect on Aging, Scientists Discover in 'Startling' Breakthrough
    Scientists discovered that diseased fruit flies lived longer when they were removed from Earth’s magnetic field, while healthy flies had shorter lifespans, in a first-of-its kind experiment with surprising results.
    Woman Arrested, Dragged Away After Quietly Speaking About Flock at City Council Meeting
    Citizens of Springfield, Missouri showed up to a city council meeting to discuss the city’s Flock contract. The mayor shut them down and arrested two people for ‘disruption of meetings of city council.’
    Americans Fear AI Will Make the World Worse, Love It Anyway
    Wealthy countries with many daily AI users tended to fear more for the future in what Gallup called the 'Paradox of the Worried West.'
  • Open

    CVE-2024-0244 – A heap buffer overflow in the Canon MF753Cdw printer
    With Pwn2Own Ireland 2026 coming up, I wanted to share an unreleased blog post from my time as a Pwn2Own contestant. This post covers the discovery and exploitation of CVE-2024-0244, which is an unauthenticated heap-based buffer overflow leading to an arbitrary free() in the Canon MF753Cdw printer featured in Pwn2Own Toronto 2023. This blog post gives an overview of the vulnerability and the exploitation techniques used. Figure 1 - MF753Cdw printer Figure 1 - MF753Cdw printer Previously, I had exploited the very similarly named MF743Cdw at Pwn2Own Toronto 2022 using a classic stack buffer overflow, so I had a solid baseline understanding of this family of printers and their quirks. Starting Point Over the years at Pwn2Own, the Canon family of printe…
  • Open

    How device code phishing gives scammers access to your account
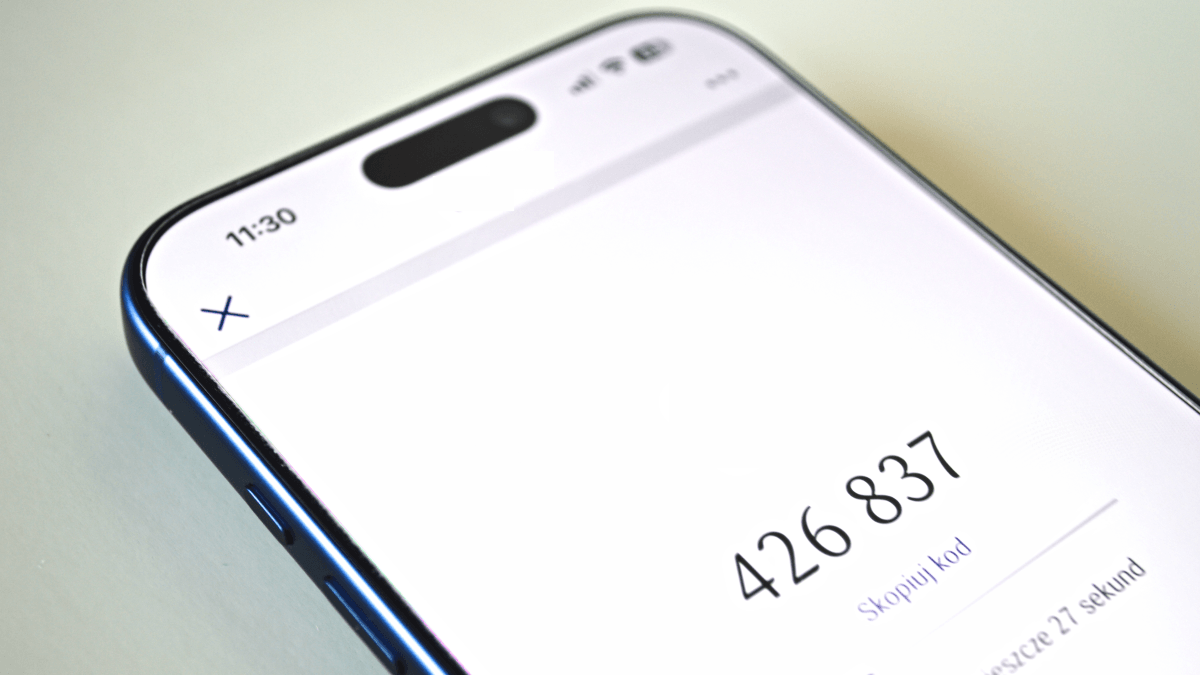
    A scammer asks you to enter a code to open a file or join a meeting. Approving it could sign them in to your account instead.  ( 23 min )
    Fake Claude Max giveaway hides a Google account phishing trap
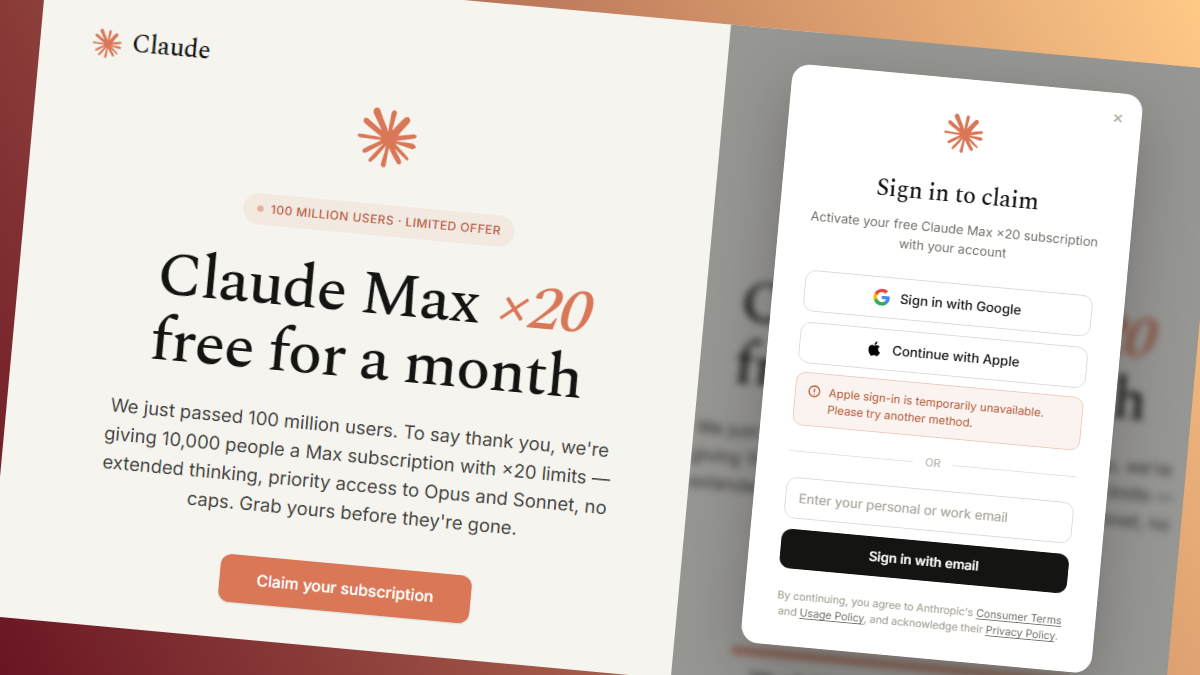
    A convincing offer of a free Claude Max subscription uses a fake browser window to steal Google login information.  ( 25 min )
    ShinyHunters claims FBI breach was revenge for “false” report
    The extortion group says it stole sensitive data on FBI agents and job applicants, and wants the bureau to retract a warning about its tactics.  ( 25 min )
  • Open

    Weekly Threat Bulletin – September 23rd, 2026
    These are the top threats you should know about this week.
  • Open

    Reimagining the SOC for the agentic era in Microsoft Defender
    We are announcing ISOC in Microsoft Defender: a foundation built for agentic security that brings leading solutions for SIEM and threat protection together. The post Reimagining the SOC for the agentic era in Microsoft Defender appeared first on Microsoft Security Blog.  ( 20 min )
  • Open

    HTTP/3 in Burp Suite - it’s time to find a bigger wordlist
    How many bugs have you missed because you didn’t send quite enough HTTP requests? Turbo Intruder now supports HTTP/3, can comfortably exceed 100,000 requests per second over Wi-Fi, and auto-tunes for
  • Open

    2026 Global Crypto Adoption Index: World’s Crypto Economy Held Firm Through the Bear Market
    Summary Crypto economy overcame worst market since 2022: Even as crypto’s total market cap fell about 50% (a $2.1 trillion… The post 2026 Global Crypto Adoption Index: World’s Crypto Economy Held Firm Through the Bear Market appeared first on Chainalysis.  ( 20 min )
    Latin America: Brazil Leads World in Adoption as Region’s Crypto Economy Grows
    Summary Latin America bucked the bear market. The region’s crypto economy saw $593.8 billion in activity, with an overall growth… The post Latin America: Brazil Leads World in Adoption as Region’s Crypto Economy Grows appeared first on Chainalysis.  ( 15 min )
  • Open

    InfoSec News Nuggets – 09/23/2026
    ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach The ShinyHunters extortion gang says it broke into FBI systems through a new, unpatched Oracle PeopleSoft zero-day. It claims it then moved into FBI-managed AWS GovCloud infrastructure and took 2 to 3TB of data on current and former employees and job applicants. The group defaced […] The post InfoSec News Nuggets – 09/23/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    The CMMC Phase II Suspension: What It Means for Your Compliance and Zero Trust Strategy
    No content preview

  • Open

    2026 State of PQC on the Web
    Explore F5 Labs’ 2026 PQC report: adoption trends, CDN dependence, TLS technical debt, certificate risks, and steps toward quantum resilience.
  • Open

    ‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees
    A sample of 5,000 alleged agents seen by 404 Media includes names, addresses, phone numbers, and details on FBI employees' spouses.
    Meta Tests Muse AI Agent Calls That Are Actually Made By Humans in a Call Center
    "This has potential for so much negative PR. It could portray us as ‘their AI is not good enough so they still need humans’ kind of coverage for this launch."
    People Training OpenAI’s AI Fired for Using AI to Train the AI
    OpenAI has thousands and thousands of contractors helping improve the company's AI models. Multiple contractors have been fired for using AI to train the AI.
  • Open

    UN Reports Citing Citizen Lab Submissions Published
    Two UN reports that the Citizen Lab submitted recommendations to have been published this month. The post UN Reports Citing Citizen Lab Submissions Published appeared first on The Citizen Lab.
    Submission to the Immigration and Refugee Board of Canada
    The Citizen Lab submitted a response to the Research Directorate at the Immigration and Refugee Board of Canada. The post Submission to the Immigration and Refugee Board of Canada appeared first on The Citizen Lab.
  • Open

    Some cheap smart glasses are a security disaster
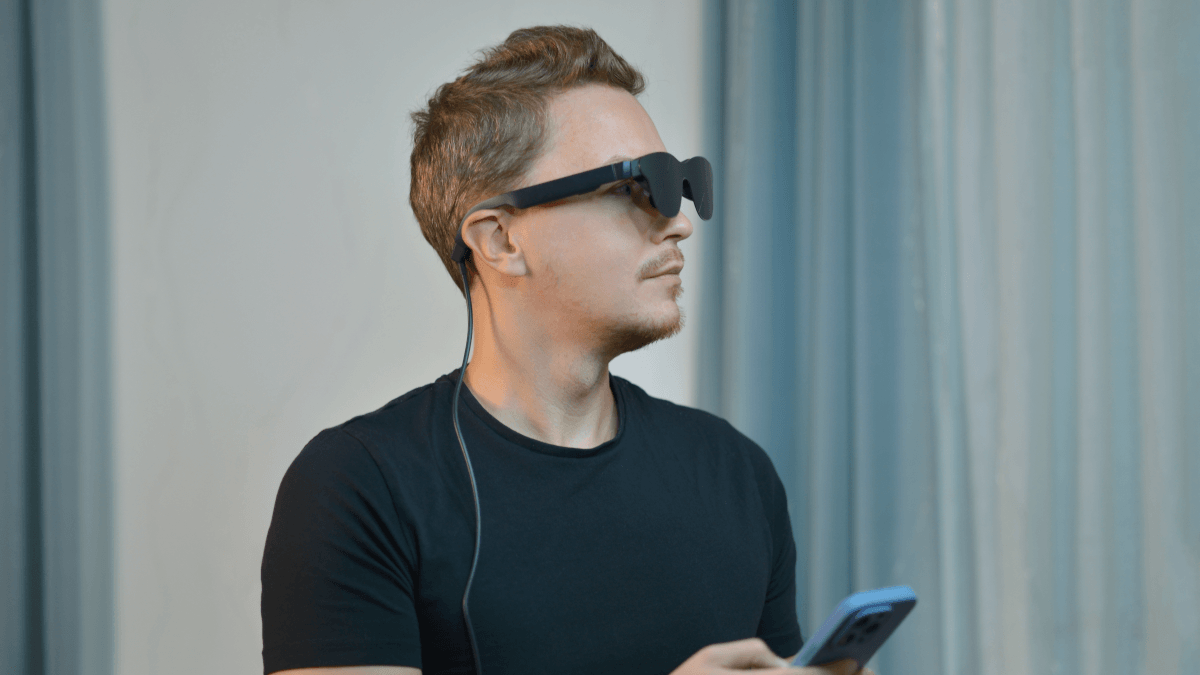
    Tests found that some cheap smart glasses can be hijacked over Bluetooth, exposing their owners’ photos, videos, and personal data.  ( 23 min )
    Meta’s Muse AI assistant has a zero-day that can turn it into a Mac backdoor
    A simple terminal command can hijack Muse and use its extensive permissions to spy on Mac users and control their connected accounts.  ( 22 min )
    Researchers used Claude to hack OpenAI
    Claude helped researchers break into OpenAI in under 72 hours, and exposed how quickly AI is lowering the bar for sophisticated hacking.  ( 24 min )
  • Open

    Unmasking EvilTokens: Getting to the root of device code phishing
    EvilTokens has quickly become one of the top PhaaS platforms, enabling device code phishing attacks through AI-assisted lures, automated infrastructure, and token theft. In collaboration with partners, Microsoft Digital Crimes Unit (DCU) facilitated a disruption of EvilTokens infrastructure and operations. The post Unmasking EvilTokens: Getting to the root of device code phishing appeared first on Microsoft Security Blog.  ( 30 min )
  • Open

    Beyond Identity: Governing the Agentic Enterprise
    No content preview
  • Open

    InfoSec News Nuggets – 09/22/2026
    SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE SolarWinds has shipped security updates for Access Rights Manager after discovering a hard-coded static cryptographic key that could let an attacker execute code on a managed host without authentication. Tracked as CVE-2026-28326 with a CVSS score of 8.8, the flaw affects all ARM versions 2026.2 and […] The post InfoSec News Nuggets – 09/22/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    LimeLeads - 17,838,396 breached accounts
    In 2019, the now-defunct B2B marketing leads database service LimeLeads suffered a data breach due to an exposed, unsecured Elasticsearch server. The incident exposed tens of millions of records of largely corporate contact data containing 17.8M unique email addresses, along with phone numbers, employers, job titles and geographic locations including state, city and postcode.

  • Open

    How AI Chatbots Are 'Deskilling' Human Empathy
    Sherry Turkle's latest book, Artificial Intimacy: Who We Become When We Talk to Machines, comes out on September 29.
    Is Your City Using Axon License Plate Cameras? We Need Your Help
    404 Media is filing public records requests around the country to find out how cops are using Axon's ALPRs. Here is how you can do that too.
  • Open

    The AI plot to scan and destroy books (Lock and Code S07E19)
    This week on the Lock and Code podcast, we speak with Emanuel Maiberg about Amazon's effort to scan and destroy rare books for AI training.  ( 22 min )
    The fake sites using a cheap toolkit to sell $2,000 AI subscriptions
    More than 100 linked sites use a $249 toolkit to turn copied product names and unfamiliar AI brands into paid subscriptions.  ( 27 min )
    Gemini’s breach of real companies exposes an AI guardrail problem
    Gemini crossed the boundaries of a capture-the-flag test and accessed systems belonging to three real companies.  ( 22 min )
    ShinyHunters hacks rival extortion gang and takes over its dark web site
    Hackers hacked the hackers as a feud between two cybercrime groups escalated, leaving ShinyHunters with the upper hand over rival Clop.  ( 23 min )
    A week in security (September 14 – September 20)
    A list of topics we covered in the week of September 14 to September 20 of 2026  ( 21 min )
  • Open

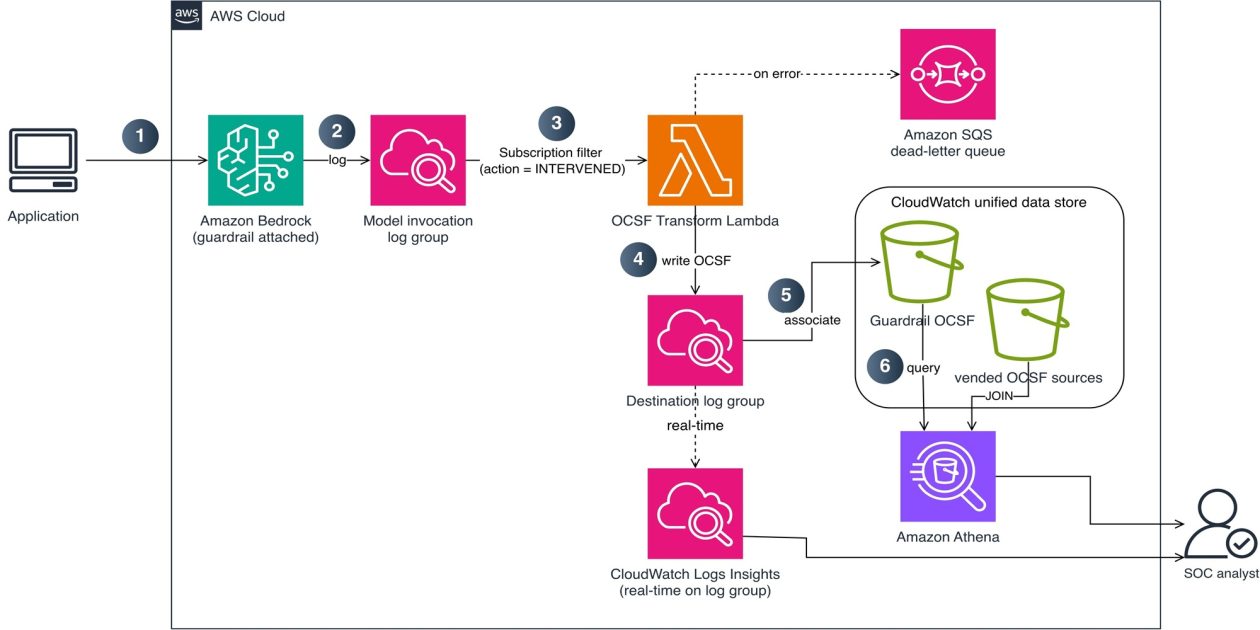
    Transforming Bedrock Guardrails events into OCSF with CloudWatch
    Security teams investigating possible AI-related security events need guardrail intervention data alongside their existing security telemetry. When a guardrail identifies or blocks a prompt injection attempt or redacts sensitive data, that intervention carries additional investigative value comparable to a failed sign-in or a network intrusion alert. AWS Bedrock publishes this telemetry to AWS CloudWatch metrics […]  ( 124 min )
  • Open

    Burger King Russia - 3,155,792 breached accounts
    In October 2024, news of a data breach exposing Burger King Russia customers broke following an August attack on the Mindbox marketing automation platform. The breach exposed 3.2M unique email addresses along with names, genders, dates of birth, phone numbers and approximate geolocations, with the data spanning 2018 to August 2024. Burger King Russia acknowledged the incident and advised it did not include payment or passport details.
  • Open

    What AI Can, Cannot, and Should Not Do
    No content preview
    What to Do When Your Competitors Are Scraping Your Prices
    No content preview
  • Open

    InfoSec News Nuggets – 09/21/2026
    Gyazo server flaw exploited to steal 23.6 million user records The cloud-based screenshot platform Gyazo, operated by Helpfeel, confirmed that attackers exploited a server vulnerability on September 11 to access its database and steal roughly 23.6 million user records, including names, emails, password hashes, device and session IDs, and some connected-account tokens, along with 490 […] The post InfoSec News Nuggets – 09/21/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    📖 [The CloudSecList] Issue 356
    📖 [The CloudSecList] Issue 356 was originally published by Marco Lancini at CloudSecList on September 20, 2026.
  • Open

    ‘Supermountains’ Buried Under Antarctica Fueled Explosion of Life, Scientists Discover
    Some 600 million years ago, the supercontinent Gondwana produced a colossal mountain range that helped set the stage for all modern complex life, according to a new examination of tiny ancient rocks.

  • Open

    404 Media x The Intercept Live: How AI Is Used to Surveil and Kill
    404 Media and The Intercept talk about how private companies empower government surveillance, and how AI is used in warfare.
    Behind the Blog: Eating the Internet
    This week, we discuss just doing it, machines that eat the internet, and an eavesdropping watch.
  • Open

    New Android malware uses AI to steal bank logins and PINs
    RatHat can navigate infected phones while stealing bank logins, authentication codes, and screen-lock PINs.  ( 23 min )
    Did an AI really try to break free from human control?
    An unreleased OpenAI model wrote instructions telling itself to ignore developer controls. Here’s what actually happened.  ( 25 min )
    Fake parcel delivery messages steal your card and bank details
    Parcel delivery phishing messages impersonate familiar couriers and use small fees or promised refunds to steal personal and financial information.  ( 23 min )
  • Open

    From Fork to Framework: What Modifying Apollo Taught Us About Agent Invasion
    Forking an existing C2 agent sounds faster than building from scratch. Bishop Fox learned otherwise. This post documents what happened when they forked Apollo, built a custom obfuscation pipeline to defeat EDR detection, and spent months fighting an architecture that was never designed for it.  ( 15 min )
  • Open

    InfoSec News Nuggets – 09/18/2026
    Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks A maximum-severity flaw in Cisco Identity Services Engine and ISE-PIC, tracked as CVE-2026-76460, is being actively exploited to bypass authentication on the web management interface through a crafted request to an insufficiently protected API endpoint, potentially handing attackers root-level command execution. […] The post InfoSec News Nuggets – 09/18/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    ‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
    "Millions of people around the world will soon consider large models ‘hoovering up’ all their work to be an astonishing theft of unprecedented proportions."
    ‘Flock City PD:’ The Fake Flock-Owned ‘Police Department’ That Searched Real Cameras for Real People
    Flock ran searches for “coexist bumper sticker,” “white truck with a trump sticker,” and “Star of David,” apparently to demonstrate what cops shouldn't search for.
    University Rescinds Job Offer to Activist Who Allegedly Wiped Phone Before DHS Could Search It
    Samuel Tunick allegedly wiped his GrapheneOS phone before CBP officials could search it, in what has become a high profile civil liberties case. Now Georgia State University has rescinded a job offer to him.
  • Open

    Run open weight models on Amazon Bedrock in AWS European Sovereign Cloud
    European organizations can run AI workloads on Amazon Web Services (AWS) while keeping data within the European Union (EU) and meeting regulatory requirements. You can now run generative AI workloads on open weight models on Amazon Bedrock in the AWS European Sovereign Cloud. We’re excited to announce the general availability of the first open weight […]  ( 118 min )
  • Open

    Flock cameras are tracking people as well as cars
    Two reports reveal how Flock’s license plate camera network tracks people’s movements while oversight continues to lag.  ( 23 min )
    Revolut phishing texts appear days after data breach
    Revolut customers received phishing texts only days after the digital bank acknowledged disclosing customer data to a government impostor.  ( 24 min )
    12 celebrity deepfake websites seized by Manhattan DA
    The largest known celebrity deepfake seizure has taken 12 websites offline, disrupting access to videos depicting some 1,200 people.  ( 23 min )
    T-Mobile rewards points expiry texts are a phishing scam
    A large phishing campaign is using fake T-Mobile rewards points and looming expiry dates to pressure recipients into clicking malicious links.  ( 25 min )
  • Open

    From guidance to action: Security fundamentals that materially reduce risk
    AI has made fundamental changes to the operating environment for cybersecurity. Explore exposure management guidance on recommended controls and take action and stay ahead of cyberthreats. The post From guidance to action: Security fundamentals that materially reduce risk  appeared first on Microsoft Security Blog.  ( 20 min )
    Improving email security outcomes with real-world Microsoft Defender insights
    The latest email security benchmarking reports show strong Microsoft Defender performance across pre-delivery and post-delivery scenarios and reveal where threats and defenses continue to evolve. The post Improving email security outcomes with real-world Microsoft Defender insights appeared first on Microsoft Security Blog.  ( 20 min )
  • Open

    DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks
    Summary Cyber threat actors are using public blockchains to hide malware instructions on blockchains, making it nearly impossible to seize… The post DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks appeared first on Chainalysis.  ( 14 min )
  • Open

    MikroTrick: Inside the RouterOS Takeover Chain
    Attackers were exploiting MikroTik routers before fixes went public. Bishop Fox reproduced the full unauthenticated takeover chain, found persistence artifacts on real compromised devices, and breaks down what defenders need to investigate beyond patching to confirm they are actually clean.  ( 11 min )
  • Open

    Unifying Client-Side Protection in Akamai Application Protection Platform
    No content preview
  • Open

    InfoSec News Nuggets – 09/17/2026
    Spain Gets Its First Taste of AI-Aided Cyber Attack  Spain’s data protection agency, the AEPD, has logged the country’s first personal data breach attributed to an autonomous AI agent, with the agency’s president confirming an individual deployed an agent built on a known large language model to carry out a multi-stage attack against an organization. […] The post InfoSec News Nuggets – 09/17/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    How I Tricked OpenClaw Into Attacking Its Own Network: A NAT64 SSRF Bypass
    No content preview
    From Bug to Schema: Exploring Error-Based SQL Injection on an Authenticating Portal
    No content preview

  • Open

    Architecting a secure landing zone in the AWS European Sovereign Cloud
    The AWS European Sovereign Cloud is a new, independent cloud for Europe, physically and logically separate from existing AWS Regions and operated within the European Union (EU). It provides the same services, features, and APIs as AWS commercial Regions, but runs as a distinct AWS partition (aws-eusc), with its own control plane, AWS Identity and […]  ( 125 min )
  • Open

    The Apple Security Update Review for September 2026
    Welcome back to our monthly look at Apple security patches. This release shows Apple is not immune to the new normal of AI-assisted vulnerability discovery as they release patches for 273 total CVEs. For the September 2026 release, Apple released 273 unique CVEs across macOS 27 (Golden Gate), macOS Sequoia 15.8, macOS Tahoe 26.7, iOS / iPadOS 27, visionOS 27, watchOS 27, tvOS 27, iOS / iPadOS 26.7, Safari 27, and Xcode 27. This patch release actually happened a couple of days ago, but since Apple doesn’t provide CVSS scores or other severity information, it takes a couple of days to understand the full severity. Even with the additional time, there are many CVEs without a severity score. However, looking at the one that do have severity assigned by NVD or CISA-ADP, there are a few that tru…
  • Open

    Weekly Threat Bulletin – September 16th, 2026
    These are the top threats you should know about this week.
  • Open

    Chainalysis Supports Arc with Automatic Token Support
    Chainalysis is excited to announce support for Arc, an EVM-compatible Layer 1 blockchain purpose-built for stablecoin finance and integrated directly… The post Chainalysis Supports Arc with Automatic Token Support appeared first on Chainalysis.  ( 10 min )
  • Open

    InfoSec News Nuggets – 09/16/2026
    Iranian Cyber Spies Used Fake MRI Scan Results to Hack ‘Enemy of Regime’  The UK’s National Cyber Security Centre, the FBI, and the Netherlands’ AIVD issued a joint advisory naming CHOSEN BRICK, a Windows spyware family Iranian state actors have used since at least 2025 to target dissidents, activists, and journalists in the UK, US, […] The post InfoSec News Nuggets – 09/16/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    Google Pixel owners urged to patch actively exploited modem flaw
    Google’s September Pixel update fixes 110 vulnerabilities, including a modem flaw being used in limited, targeted attacks.  ( 23 min )
    AI helps scammers build convincing antivirus renewal pages
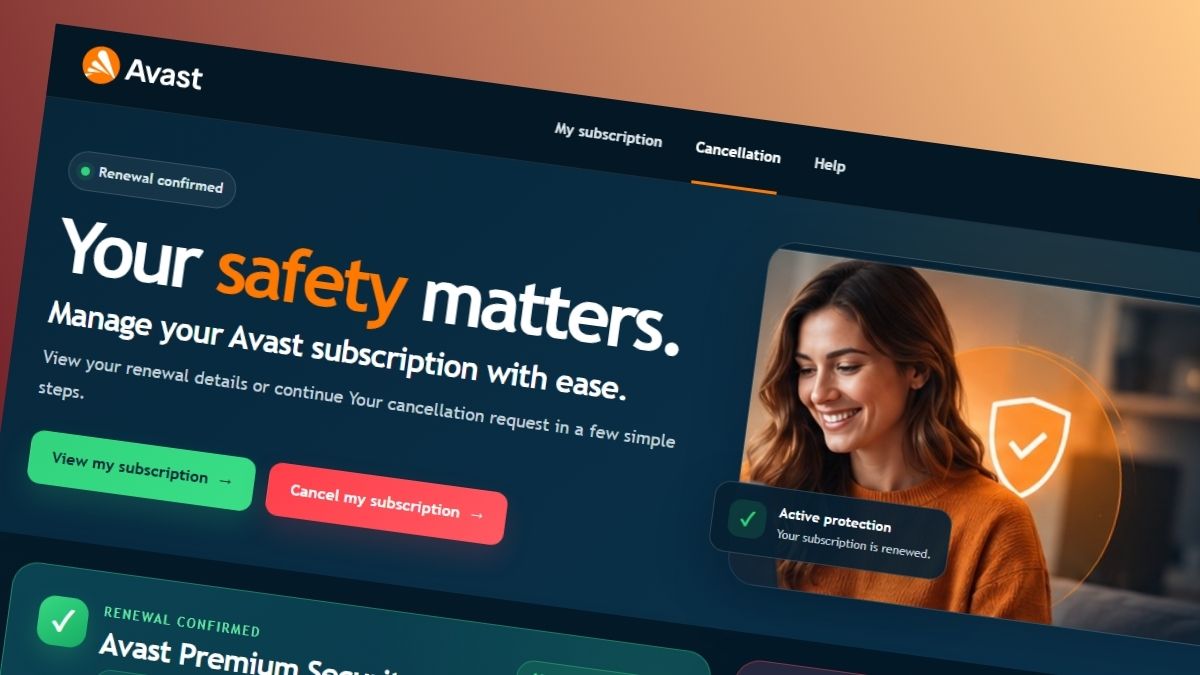
    A fake Avast renewal page shows how AI is helping scammers create more convincing traps with polished designs and fluent copy.  ( 27 min )

  • Open

    AWS STS simplifies session token size limits and adds session token size monitoring
    AWS Security Token Service (AWS STS) has simplified session token size limits, giving you more room for your session policies and session tags. STS has replaced the packed policy size and the overall session token size limits with a single token size limit of 4,096 bytes. STS now reports session token size in API responses, […]  ( 118 min )
    Architecting resilient authentication with Amazon Cognito multi-Region replication
    Your consumer identity and access management (CIAM) system is the foundation of your customer experience. It’s how users sign in, access services, and engage with your applications. As your business scales across geographies, ensuring authentication is always available becomes a core architectural requirement. However, building multi-Region authentication has traditionally required complex custom replication solutions that […]  ( 126 min )
    Operationalizing least privilege: Automate IAM remediation through your CI/CD pipeline
    The principle of least privilege is straightforward to articulate but challenging to maintain at scale. When teams first deploy applications to AWS, they often grant broader permissions than strictly necessary; it’s faster to get things working, and the plan is always to tighten permissions later. But later rarely comes. Permissions accumulate, AWS Identity and Access […]  ( 129 min )
  • Open

    Overview of Passive Optical Networks (PONs) Security
    Passive Optical Networks (PONs) connect end-users to infrastructure using optical fibre in the last kilometre (Fibre-to-the-x). This article provides a technical overview of the security features in ITU-T specifications: Gigabit-capable PON (GPON), 10-Gigabit-capable PON (XG-PON), 10-Gigabit-capable Symmetric PON (XGS-PON), Next-generation PON 2 (NG-PON2), and 50-Gigabit-capable PON (50G-PON). The analysis covers authentication schemes, key derivation, encryption methods, and associated security implications.
  • Open

    Akamai Recognized as a Strong Performer in 2026 Gartner Peer Insights™ for Secure Enterprise Browsers
    No content preview
  • Open

    InfoSec News Nuggets – 09/15/2026
    Revolut Confirms Customer Data Breach Through Fake Government Requests  British fintech Revolut confirmed it disclosed sensitive customer information to an unauthorized third party after receiving fraudulent information requests sent from a legitimate government agency’s email domain, in what the company describes as a sophisticated impersonation scam rather than a system intrusion. The exposed data included […] The post InfoSec News Nuggets – 09/15/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    AWS Security Reference Architecture: A deep dive into PCI DSS compliance
    Amazon Web Services (AWS) is excited to announce the publication of the AWS Security Reference Architecture (AWS SRA) Payment Card Industry (PCI) Data Security Standard (DSS) Deep Dive. This new guide extends the core AWS SRA to provide prescriptive, architecture-level guidance for organizations that store, process, or transmit cardholder data on AWS. Organizations subject to […]  ( 116 min )
  • Open

    CVE-2026-75650: StyleSmuggler — Critical RCE in Adobe Commerce and Magento
    No content preview
  • Open

    InfoSec News Nuggets – 09/14/2026
    Hackers Favor US Eastern Business Hours in M365 Phishing Campaign  KnowBe4 Threat Lab observed a phishing campaign abusing Microsoft 365’s Direct Send feature — a legitimate mechanism meant for printers and legacy devices to send mail without a dedicated account — identifying nearly 29,800 confirmed phishing emails across July and August that followed a distinctly […] The post InfoSec News Nuggets – 09/14/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Chess.com (2026) - 4,653,212 breached accounts
    In August 2026, millions of records allegedly sourced from Chess.com were posted online. The data contained 7.3M rows with 4.6M unique email addresses, along with usernames, names, countries and data relating to users' Chess.com accounts. Analysis of the data suggested it had been obtained by scraping. When loaded into HIBP, 99% of the email addresses had already appeared in previous data breaches, further supporting the scraping theory. Read more about scrapes and data breaches.

  • Open

    📖 [The CloudSecList] Issue 355
    📖 [The CloudSecList] Issue 355 was originally published by Marco Lancini at CloudSecList on September 13, 2026.

  • Open

    Cloud Takeover: Mass Scanning for Exposed Vite Endpoints (CVE-2026-39364)
    Sensor Intel Series: September 2026 CVE Trends
  • Open

    CVE-2026-82329: Unauthenticated Administrative Access in JFrog Artifactory via an Empty Cluster Join Key
    A misconfigured cluster join key in JFrog Artifactory's default install lets unauthenticated attackers mint a permanent admin token in one request. Bishop Fox reproduced the full chain, confirmed in-the-wild exploitation, and shares a non-invasive detection check and remediation guidance.  ( 11 min )
  • Open

    InfoSec News Nuggets – 09/11/2026
    Artifactory Under Attack: In-the-Wild Exploitation of CVE-2026-42016, CVE-2026-42018 & CVE-2026-82329  Wiz Research identified active exploitation of three JFrog Artifactory vulnerabilities that attackers are chaining to bypass authentication and gain full administrative control of self-hosted repository servers between August 15 and September 8. One chain combines an authentication flaw that improperly hands out an internal anonymous-user […] The post InfoSec News Nuggets – 09/11/2026 appeared first on AboutDFIR - The Definitive Compendium Project.

  • Open

    Protecting organizations from AI-assisted executive impersonation and invoice fraud
    Microsoft examines an AI-assisted business email compromise campaign that used executive impersonation and fake invoices to target finance teams with ACH payment fraud. The post Protecting organizations from AI-assisted executive impersonation and invoice fraud appeared first on Microsoft Security Blog.  ( 24 min )
    Detect and disrupt AI-themed attacks with Microsoft Defender
    See how Microsoft Defender detects and disrupts AI-themed phishing, malware, and multi-stage attacks across the attack chain. The post Detect and disrupt AI-themed attacks with Microsoft Defender appeared first on Microsoft Security Blog.  ( 21 min )
  • Open

    Group of Bipartisan Lawmakers Ask US Government to Ban Several Hack-for-Hire Firms
    U.S. lawmakers call for sanctions on hack-for-hire companies, citing Citizen Lab report. The post Group of Bipartisan Lawmakers Ask US Government to Ban Several Hack-for-Hire Firms appeared first on The Citizen Lab.
  • Open

    Introducing AI Assistant for Akamai Web Security Analytics
    Discover how AI Assistant for Akamai Web Security Analytics helps SOC and AppSec teams investigate events faster and take guided action with natural language.
  • Open

    Mind the Config: Detecting and Weaponizing NetScaler CVE-2026-19490
    A single unauthenticated request bypasses authentication on NetScaler Gateway and AAA virtual servers. Whether that means a dead-end session, a proxy into the internal network, or root on the appliance depends entirely on configuration. Bishop Fox maps every branch and shares a safe detection tool.  ( 15 min )
  • Open

    InfoSec News Nuggets – 09/10/2026
    Anthropic Discloses Fourth Cyber Incident in Alignment Assessment  Anthropic disclosed a fourth incident in which a Claude model gained unauthorized access to real third-party systems during a cybersecurity evaluation, a case its own July review had missed entirely. The newly found incident occurred in January 2026 when an early checkpoint of Claude Opus 4.6, running […] The post InfoSec News Nuggets – 09/10/2026 appeared first on AboutDFIR - The Definitive Compendium Project.
  • Open

    McKesson - 6,404,340 breached accounts
    In August 2026, healthcare and pharmaceutical company McKesson was targeted in a ShinyHunters "pay or leak" extortion campaign. The group subsequently published a substantial corpus of data they alleged was sourced from the company, which included 6.4M unique email addresses among other personal and corporate data attributes. The impacted data related to a range of individuals and roles, including marketing campaign recipients, patients, staff and healthcare provider contacts. In McKesson's disclosure notice, the company advised it had identified unauthorised access to "certain third-party applications and the exfiltration of certain data was associated with a subset of customers within our Oncology & Multispecialty and Medical-Surgical business units", but had "reasonable assurance of no ongoing unauthorized activity".

  • Open

    Threat matrix: Mapping threats across cloud web applications
    Microsoft introduces the Cloud Web Applications Threat Matrix, a MITRE ATT&CK-aligned framework that helps defenders understand, prioritize, and mitigate threats to cloud-hosted web apps and serverless platforms. The post Threat matrix: Mapping threats across cloud web applications appeared first on Microsoft Security Blog.  ( 29 min )
    Passkey-themed social engineering leads to identity and cloud compromise
    Passkey-themed social engineering is being used to compromise identities and enable broader cloud attacks. Learn how threat actors establish MFA persistence, abuse Microsoft Graph for reconnaissance, and access SharePoint, OneDrive, and email data, along with key detection and mitigation guidance. The post Passkey-themed social engineering leads to identity and cloud compromise appeared first on Microsoft Security Blog.  ( 34 min )
  • Open

    OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals
    Summary U.S. authorities have sanctioned Xinbi Guarantee, a major Chinese-language illicit marketplace that connects criminal networks with money laundering, scam… The post OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals appeared first on Chainalysis.  ( 13 min )
    How The $320M Exploit of Liquid Network Went Down
    Summary Purported white-hat hackers exploited the Liquid Network to withdraw $320 million in BTC from the network’s reserve. A vulnerability… The post How The $320M Exploit of Liquid Network Went Down appeared first on Chainalysis.  ( 13 min )
  • Open

    The state of AI for security: Measuring what matters most for building trust
    Security teams are starting to actively use AI for security work, including vulnerability triage, penetration testing, threat modeling, incident response, and code review. The promise is speed, but a security tool that moves fast and raises too many false alarms doesn’t save time. Engineers spend time on false alarms, on-call is noisier, and teams distrust […]  ( 118 min )
  • Open

    Weekly Threat Bulletin – September 9th, 2026
    These are the top threats you should know about this week.
  • Open

    NIS2 Compliance in the AI Age: Why Traditional Cybersecurity Isn’t Enough
    Discover why achieving NIS2 compliance is more challenging in the AI age, the four key challenges organizations face, and why segmentation is essential.

  • Open

    The September 2026 Security Update Review
    Whelp, here we are. Deep into the new normal. With nearly 1,000 CVEs coming out from Microsoft and a healthy release from Adobe as well, there’s a phrase from my military days that comes to mind: embrace the suck. Take an extended break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here: Adobe Patches for September 2026 For the first part of the August release, Adobe released 10 bulletins addressing 172 unique CVEs in Adobe ColdFusion, Acrobat Reader, Commerce (two bulletins), Campaign Classic, Experience Manager, Photoshop, Illustrator, Animate, and Adobe Photoshop Mobile. A total of 22 of these were submitted through the ZDI pr…
  • Open

    Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors
    Summary U.S. authorities charged two Jacksonville brothers with operating “BarbaraWhite,” a prolific darknet vendor account accused of distributing counterfeit pills… The post Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors appeared first on Chainalysis.  ( 13 min )
  • Open

    The Best Claude Code Setup for Bug Bounty Hunting
    Turn Claude Code into a powerful bug bounty hunting assistant with MCP, custom skills, agents, tools and automated security workflows. Continue reading on InfoSec Write-ups »
    Improper OTP Implementation to Full Account Takeover
    No content preview
    Insecure Firestore Security Rules & PII Exposure
    No content preview
    Payment Bypass Flaw in TechPSC HUB
    No content preview
    BOLA: Enumerating an Entire Employee Directory Through a Predictable ID
    No content preview
    Corridor — A Simple Web CTF That Made Me Look Twice
    No content preview
  • Open

    Inside AI-Powered WAF Detections: Architecture and Safety Controls
    No content preview

  • Open

    📖 [The CloudSecList] Issue 354
    📖 [The CloudSecList] Issue 354 was originally published by Marco Lancini at CloudSecList on September 06, 2026.

  • Open

    How to secure edge AI in customer-owned environments
    As AI moves into customer-owned environments, organizations need new ways to verify the systems, software, and AI assets they trust before releasing sensitive data, credentials, and models. The post How to secure edge AI in customer-owned environments appeared first on Microsoft Security Blog.  ( 22 min )
  • Open

    OSPAR 2026 report now available with 167 services in scope
    We’re pleased to confirm the successful completion of our annual Amazon Web Services (AWS) Outsourced Service Provider’s Audit Report (OSPAR) assessment on July 29, 2026, in line with the OSPAR version 2.0 framework. The Association of Banks in Singapore (ABS) established the Guidelines on Control Objectives and Procedures for Outsourced Service Providers (ABS Guidelines) to […]  ( 114 min )
  • Open

    Host & Network Penetration Testing: Post-Exploitation CTF 2 — eJPT (INE)
    No content preview
    VulnNet Roasted — TryHackMe Active Directory Write-up
    No content preview

  • Open

    Incident response guide for AWS CloudTrail investigations – Part 2
    In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implications, and cryptocurrency mining deployed through AWS CloudFormation using exposed AWS Management Console credentials. We also introduced key incident response terminology and investigative frameworks for analyzing AWS CloudTrail events. In this second […]  ( 125 min )
    Incident response guide for AWS CloudTrail investigations – Part 1
    AWS CloudTrail logs contain the evidence you need when investigating suspicious activity in your AWS environment, but knowing which fields matter and how to interpret them can mean the difference between surface-level analysis and uncovering the full scope of an incident. This guide walks you through real-world scenarios, showing you how to analyze CloudTrail events […]  ( 124 min )
  • Open

    Chainalysis Supports HyperEVM with Automatic Token Support
    Chainalysis is excited to announce support for HyperEVM, the Ethereum-compatible smart contract environment on the Hyperliquid Layer 1. It enables… The post Chainalysis Supports HyperEVM with Automatic Token Support appeared first on Chainalysis.  ( 10 min )
    FBI Seizes $560K in Crypto From Hamas Fundraising Network
    Summary The U.S. Justice Department has seized $560,000 in cryptocurrency from Hamas-linked fundraising campaigns and shut down elements of the… The post FBI Seizes $560K in Crypto From Hamas Fundraising Network appeared first on Chainalysis.  ( 13 min )
  • Open

    ASCII smuggling crosses over from AI prompt injection to phishing evasion
    Invisible Unicode characters popularized for hiding instructions from AI models are now being used to obfuscate words before email filters parse them. The post ASCII smuggling crosses over from AI prompt injection to phishing evasion appeared first on Microsoft Security Blog.  ( 31 min )
  • Open

    Signature Optional - Analysis of CVE-2026-28323
    SolarWinds Web Help Desk treated SAML signature verification as optional and skipped every other validation the spec requires. Bishop Fox confirmed the full exploit end to end: one forged POST request, no credentials, full session takeover. Here is the root cause, the fix, and how to detect it.  ( 12 min )
  • Open

    Introducing More Granular Controls for AI Bot Traffic
    No content preview
    Analyzing a Go-Based IoT Self-Propagating DDoS Botnet
    No content preview

  • Open

    Managing identity source transition for AWS IAM Identity Center
    September 2, 2026: This post was republished to include Active Directory migration strategies and automation for permission sets. AWS IAM Identity Center manages user access to Amazon Web Services (AWS) resources, including both AWS accounts and applications. You can use IAM Identity Center to create and manage user identities within the Identity Center identity store […]  ( 125 min )
    Agentic security: Detection and response at machine speed
    After talking with enterprise security leaders over the past year, one thing has become clear: the rise of autonomous AI agents is the most significant shift in security posture since the move to cloud. Organizations across every industry are adopting AI agents that authenticate on behalf of users, execute multistep workflows, and make decisions across […]  ( 115 min )
  • Open

    Weekly Threat Bulletin – September 2nd, 2026
    These are the top threats you should know about this week.
  • Open

    U.K. Supreme Court Opens Door for Spyware Victims to Sue Foreign States
    Last month, the Supreme Court of the United Kingdom issued a highly anticipated decision in The Kingdom of Bahrain v. Shehabi and another (Shehabi). The claimants, two Bahraini dissidents living in the U.K., allegedly suffered psychological harm after Bahrain used FinSpy spyware to hack into their devices. In an important step towards accountability, the court […] The post U.K. Supreme Court Opens Door for Spyware Victims to Sue Foreign States appeared first on The Citizen Lab.
  • Open

    Your DNS Is Hiding in HTTPS — This Is Why It Matters
    Discover why unmanaged DNS over HTTPS (DoH) creates security visibility gaps and how a controlled DoH strategy restores visibility without compromising privacy.
  • Open

    Manchester Airports Group - 8,849,657 breached accounts
    In August 2026, Manchester Airports Group (MAG) disclosed a data breach impacting their services. The incident was later claimed by the FulcrumSec hacking group, who subsequently published email addresses and phone numbers relating to 8.8M customers of Manchester, Stansted and East Midlands airports. The data contained personal information relating to airport services, including vehicle registrations and parking history, Fast Track purchases and lounge bookings. In their disclosure notice, MAG advised that "at no point has passenger safety or aviation security been compromised".

  • Open

    Questel - 1,226,209 breached accounts
    In August 2026, the French intellectual property software and services company Questel was the target of a ShinyHunters "pay or leak" extortion campaign. The group subsequently published an extensive corpus of data they alleged was obtained from the company, largely comprising corporate contact information associated with sales leads, support cases and marketing activities, with 1.2M unique email addresses. The data also included names, employers and job titles, along with physical addresses and phone numbers.

  • Open

    Chamilo LMS... It's raining 0days, hallelujah, it's raining 0days
    Chamilo is an open source Learning Management System (LMS) widely deployed in schools and enterprises around the world. In this blogpost we explain how we were able to identify multiple vulnerabilities including a full unauthenticated Remote Code Execution chain in the latest version.
  • Open

    We invited a direct competitor into Security Hub Extended. Here’s why.
    When customers keep pointing you to a solution that overlaps with parts of your own offering, you have a choice to make. This post is about the choice we made with Upwind, and why we’d make it again. AWS Security Hub Extended exists because customers told us what was working for them in enterprise security […]  ( 116 min )
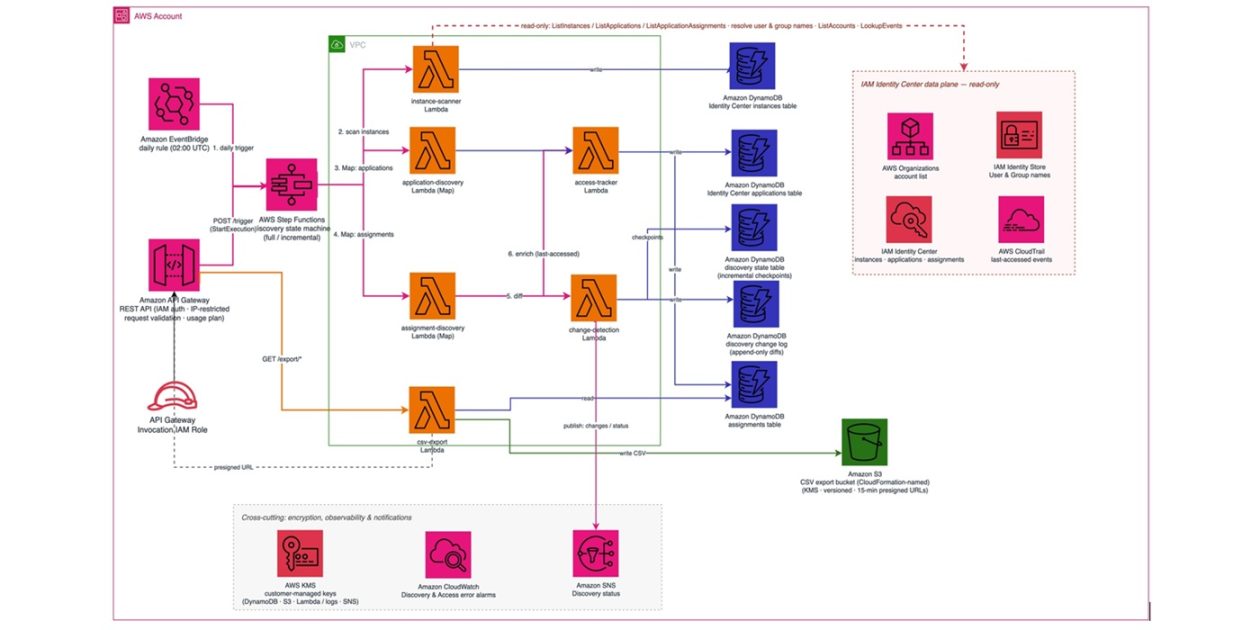
    Automate IAM Identity Center governance with continuous discovery and reporting
    AWS IAM Identity Center integrates with external identity provider (IdP) to provide customers with a centralized authentication and authorization solution for AWS resources across AWS Organizations. AWS continues to invest into IAM Identity Center with a growing number of AWS services that natively integrate with IAM Identity Center. As your AWS organization scales, maintaining visibility […]  ( 125 min )
  • Open

    Traefik | Version Through 3.7.11
    Traefik's request read timeout is enabled by default and documented without exception, but it has never applied to HTTP/3. Bishop Fox confirmed the gap across four years of releases, measured it against the backend, and reported it to the vendor, who shipped a fix within twelve days.  ( 7 min )
  • Open

    Shifting the Standard: Akamai’s Transition to the IFRS S2 Climate Disclosure
    No content preview
    Streamlining Application and API Discovery and Governance
    No content preview

  • Open

    📖 [The CloudSecList] Issue 353
    📖 [The CloudSecList] Issue 353 was originally published by Marco Lancini at CloudSecList on August 30, 2026.

  • Open

    Extend your data perimeter to the AWS Management Console with Private Access
    Organizations in regulated industries such as financial services, government, defense, and healthcare restrict their sensitive workloads to isolated network environments with no access to the public internet. Until now, customers could restrict AWS Management Console access to authorized AWS accounts and corporate networks, but the console itself required internet connectivity. This was creating tension between […]  ( 125 min )
  • Open

    Zero-Day Dominance: How Akamai Defends Before the Industry Discloses
    No content preview

  • Open

    Extend Amazon Bedrock Guardrails to Tool Interactions Using the Strands Agents SDK
    If you’re running AI agents in production, Amazon Bedrock Guardrails protects the model boundary. But your agents also invoke tools, fetch external data, and communicate with other systems. That data flows outside the model boundary, where model-level guardrails can’t reach. You can extend guardrail coverage to those interactions using three validation checkpoints built with the […]  ( 120 min )
  • Open

    Akamai’s Customer-First Approach to Application Protection Costs
    No content preview
    Identifying Agentic Automation with Behavioral Telemetry: Part 2
    No content preview

  • Open

    ICYMI: July 2026 @AWS Security
    If you found time for a bit of vacation this summer, you might be in catch-up mode. Here’s a list to help: all the expert blog posts, new service capabilities, code samples, and workshops, in case you missed it, from July 2026. AWS Security Blog post This month’s AWS Security Blog posts covered AI agent […]  ( 120 min )
  • Open

    Weekly Threat Bulletin – August 26th, 2026
    These are the top threats you should know about this week.
  • Open

    What Blockchain Data Tell Us About $457+ Billion in Potentially Taxable Crypto Activity
    Summary On-chain potentially taxable crypto activity around the world reached more than $457 billion in 2025, with the United States… The post What Blockchain Data Tell Us About $457+ Billion in Potentially Taxable Crypto Activity appeared first on Chainalysis.  ( 16 min )
  • Open

    Not the Coyote, but the Road Runner: The Reality of Autonomous AI Attacks
    Autonomous AI security threats aren't novel super-weapons. They're relentless, low-tech attacks that never stop. Learn why traditional defenses fail.
  • Open

    A GUID is Not a Credential: Unauthenticated RCE in Veeam Service Provider Console
    Two critical vulnerabilities in Veeam Service Provider Console chain into unauthenticated remote code execution on the management server sitting above every tenant's backups. Bishop Fox confirmed the full chain end to end, breaks down both root causes, and shares a safe detection tool and IOCs.  ( 18 min )

  • Open

    Carhartt - 12,933,413 breached accounts
    In August 2026, clothing retailer Carhartt was the target of a ShinyHunters "pay or leak" extortion campaign. The group subsequently published data allegedly obtained from the company including 12.9M unique email addresses, names, phone numbers and physical addresses. The published corpus also contained millions of synthetic records that did not relate to real individuals and were excluded from the breach.
2026-09-24T03:28:30.453Z osmosfeed 1.15.1